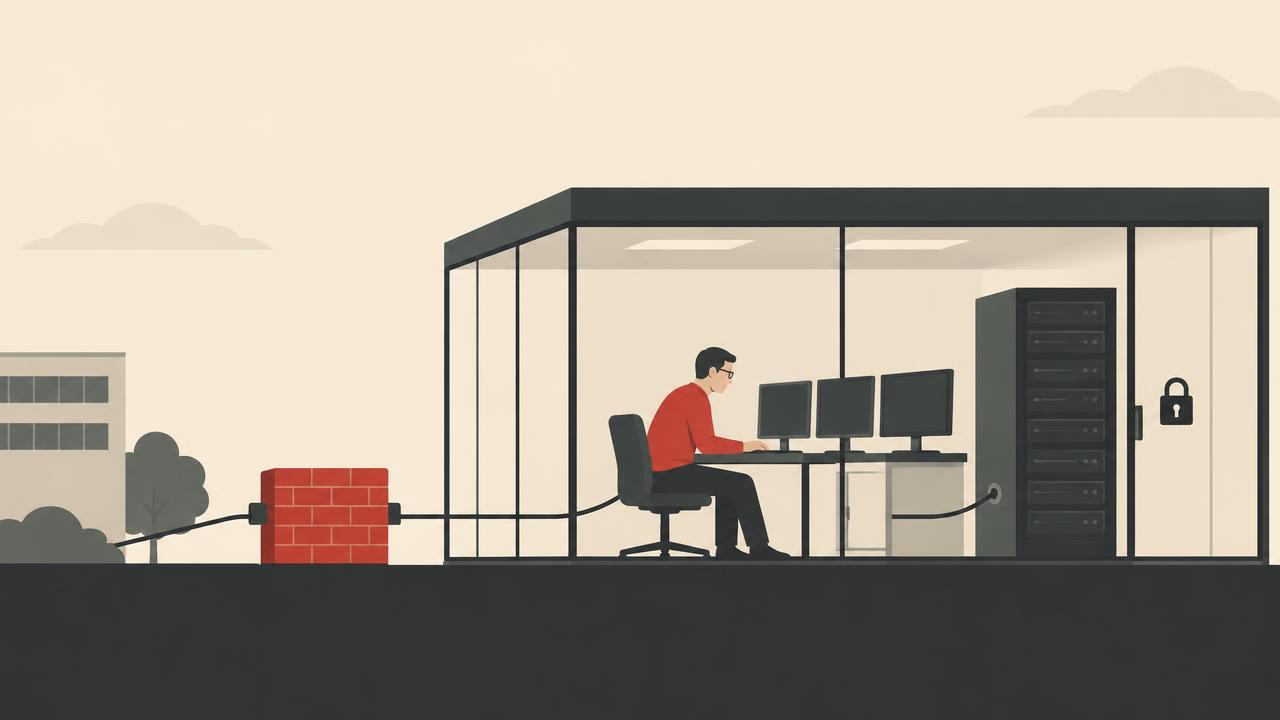
An approach developed with AI research lab Prime Radiant runs code executed by coding agents in a dedicated sandbox while leaving the agent itself outside it. Among its aims is to make experimentation with local models safer by reducing the risk that a mistake or prompt injection attack leads to damaging actions on a computer.
Prime Radiant, the lab behind Superpowers and other projects, introduced the external sandbox pattern in a blog post. Three sandbox server implementations have been released to demonstrate it:
- external-sandbox-v86 uses a Node.js server and v86 to run Alpine Linux inside WebAssembly.
- external-sandbox-container is a Python web server that runs Alpine Linux in an Apple Containers instance.
- external-sandbox-quicksand is also a Python web server; it uses Microsoft’s Quicksand sandboxing library, which bundles QEMU and Alpine Linux in a Python package.
All three implementations offer the same localhost API. Pi, Claude Code and Codex can be configured to call the sandbox through that API whenever they need to execute code.
The sandboxes also include an optional HTTP/HTTPS proxy that uses an allow-list to control which hosts the agent’s code can contact. A credential replacement mechanism enables authenticated API calls without sharing the secret with the agent. The proxy can be reconfigured through an interface while the sandbox is running.
The external sandbox pattern also provides a way to experiment with different isolation approaches while exploring the challenge of running untrusted code safely.